

Sign in
Go to ddepot.cedarai.com, or open Data Depot from Cedar Accounts. If you aren’t signed in, Data Depot sends you to the Cedar sign-in page and brings you back afterwards. Your name and email appear in the top right, next to Sign out.Roles
Most people need a single role, Data Depot Admin, granted on each carrier they work with.
After a role is granted, sign out of Data Depot and sign in again so your new access is picked up.
Your organization’s Admin Portal administrator can grant these roles. If no one in your organization can, contact your
Cedar account team. See Roles for how roles and bindings work in the Admin Portal.
What each action needs
If you build custom roles in the Admin Portal, use this table to choose permissions. Data Depot Admin includes all of them.
The MCP pages don’t need a Data Depot permission. What your AI assistant can read through MCP comes from your
existing ARMS permissions for each carrier. See MCP.
If you don’t have access
When something is missing, Data Depot tells you instead of showing an empty page.
If you can’t open Postgres for the selected carrier, Data Depot takes you to API or MCP instead, whichever you
can use.
If you can see but not change
Some roles let you look without changing anything. For example,dataDepot.provision.read lets you browse Postgres
sources and views but not create them. On those pages, Data Depot shows one bar at the top, such as View only on
Postgres, that says what you can’t do and which role to ask for. The buttons for actions you can’t take stay on the
page but are turned off, so you can still see what the option offers. On a source’s page, Choose columns becomes Columns and shows which
columns are Included in the current view.
View as a user group
View as user group lets an admin check what Data Depot looks like for members of one of the carrier’s user groups, for example before granting a group access. It appears in the header when you have theiam.userGroupPolicy.viewAs permission and the carrier has at least one user group. Carrier admin and operator roles
include this permission.
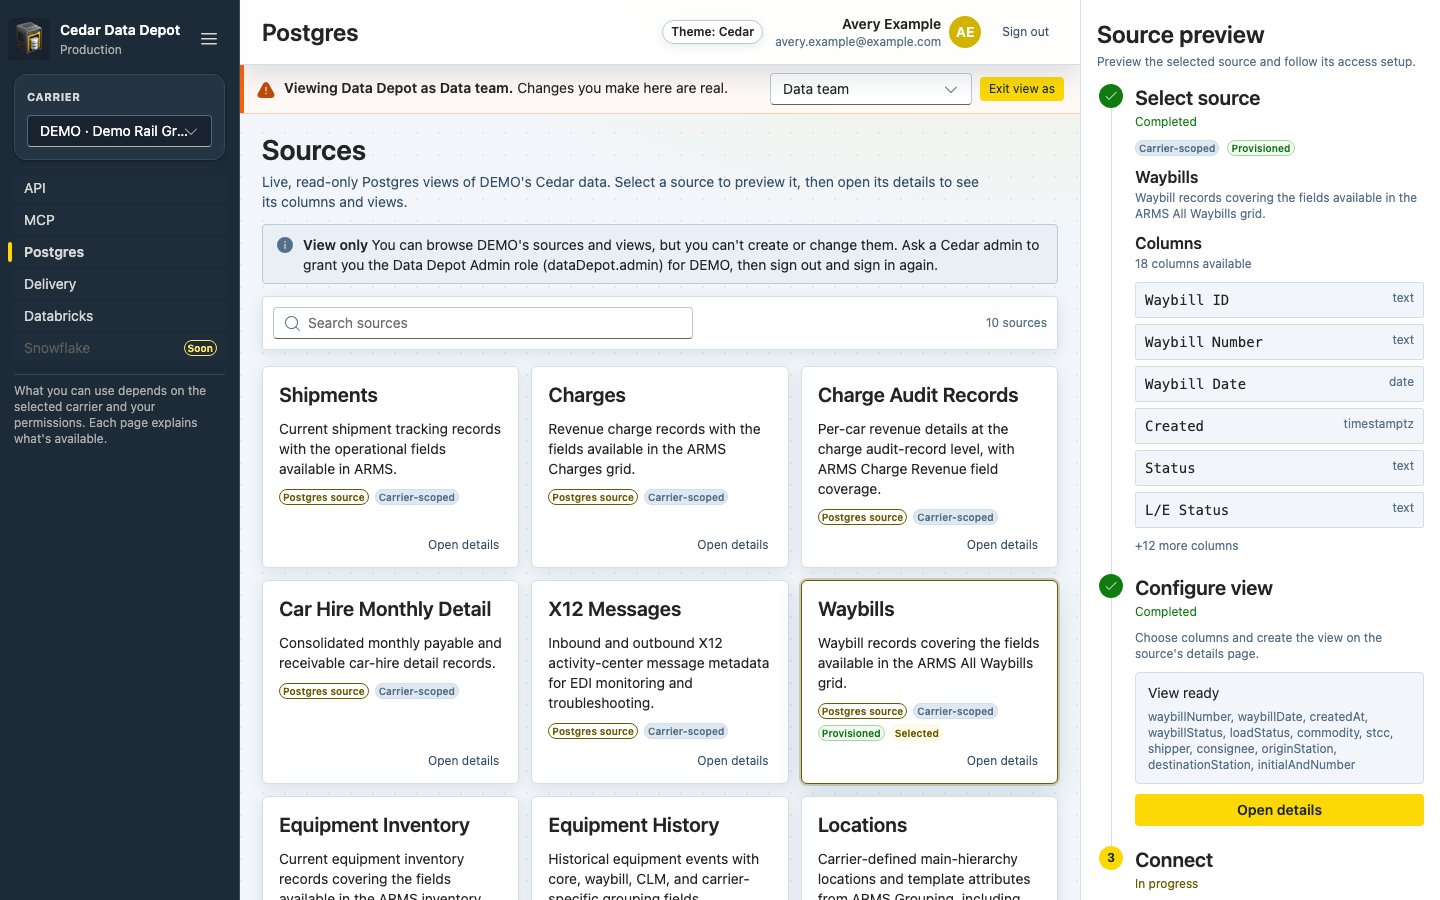
Viewing Data Depot as the Data team user group. This group can only view Postgres, so the page shows a View only bar.
1
Start View as
Select View as user group in the header. Data Depot starts with the carrier’s first user group and shows a
banner that names it, for example Viewing Data Depot as Data team. Changes you make here are real.
2
Pick the group
To check a different group, choose it from the list in the banner. You can pick any user group on the carrier, not
just groups you belong to. Every page now uses that group’s permissions.
3
Exit
Select Exit view as to return to your own permissions.